Topics inside this course
Awareness and induction depth — not an accredited occupational qualification.
- Unique passwords versus reuse
- Password managers versus spreadsheets
- MFA: something you have; never share the code
- Push fatigue and fake login pages
- Work versus personal on shared devices
Built for the people who take the training
Anyone with a work login, including contractors and executives who still reuse passwords.
What learners leave able to do
- Use unique passwords and a password manager as the organisation requires
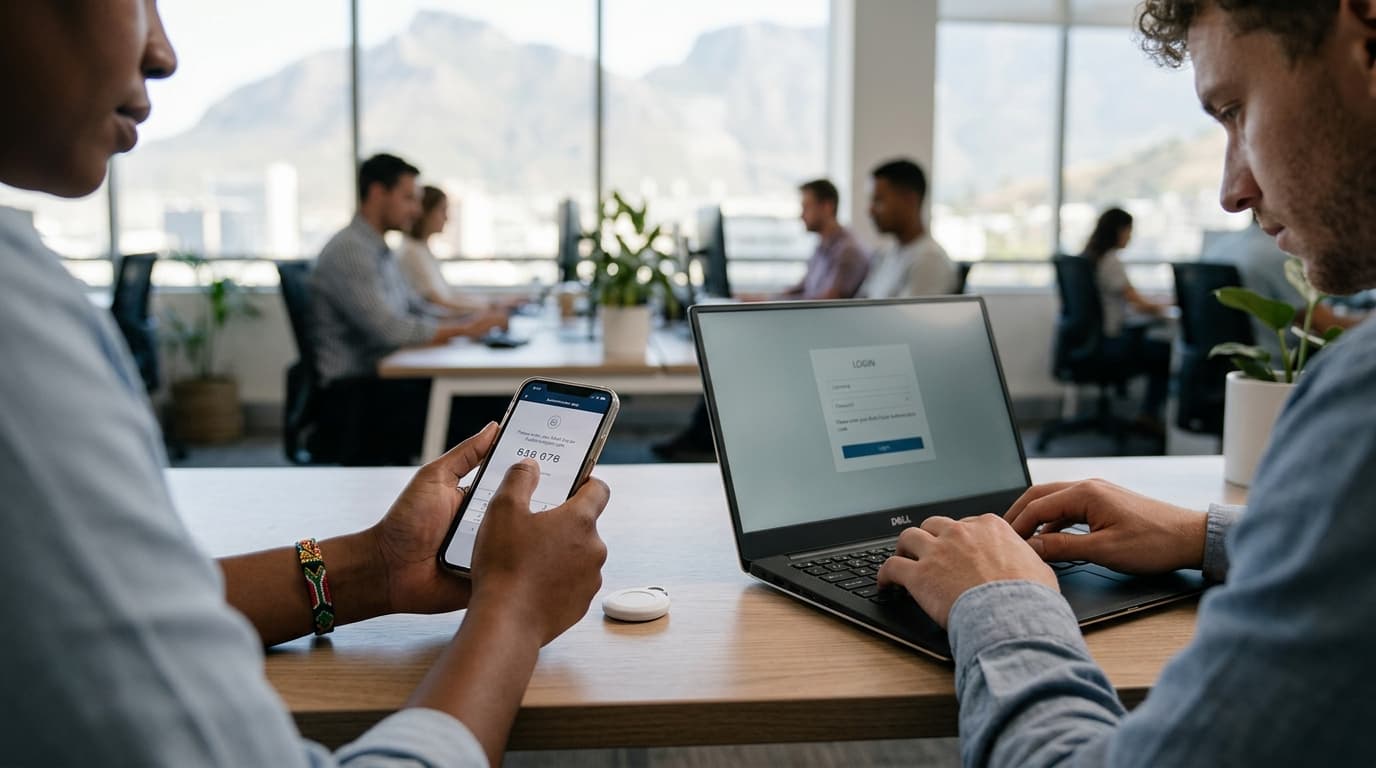
- Turn on and use MFA without sharing OTPs or approving mystery prompts
- Recognise login pages and prompt-bombing as phishing
- Separate work and personal accounts on shared devices
Modules you can expect
Structure may tighten when you localise from your own source pack in Kre8AI — this is the shape of the library title.
- 1Secrets that don’t travel
Reuse is how one breach becomes many.
- 2Managers
The organisation’s approved way to remember.
- 3MFA
Enrol, use, don’t share.
- 4When MFA is the attack
Prompt bombing and fake pages.
- 5Knowledge check
Short scored assessment.
Short scored assessment. Follow the customer authentication standard when it is stricter than NIST. Not product training for a single vendor unless the policy names it.
Written for the workplace, not for the statute book alone
Password courses fail when they still teach quarterly complexity soup that people write on pads. This module follows current public guidance: length, uniqueness, managers, MFA — then defers to your authentication standard when it is stricter.
Learners practise never sharing an OTP, never approving a prompt they did not initiate, and never using the same secret for email and the bank. Executives are in scope because their accounts are the ones attackers want.
Phishing that steals MFA is covered lightly; the phishing course owns depth. This title stays short enough for annual assignment next to the wider cyber awareness course.
Generate from NCSC/NIST extracts and your MFA enrolment guide in Kre8AI so the authenticator app or hardware token you actually issue is named. Publish as SCORM or HTML.
Re-export when you change MFA product or drop forced rotation. Do not leave a 2012 complexity slide in the LMS.
Play the library demo, or generate passwords-and-MFA from your authentication standard in Kre8AI.
What you would upload in Kre8AI
Authentication standard, MFA enrolment guide
- NCSC password and MFA guidance
- NIST SP 800-63B selected recommendations
- Your authentication standard and MFA enrolment guide
Formats, coach and provenance
- Standalone HTML to play in the browser; SCORM 2004 for your LMS.
- Optional AI course coach on Growth and Scale — grounded in approved material; off on quizzes and final assessment by default. Course plays offline; coach needs a network.
- Built in Kre8AI and reviewed before we published it. Not a substitute for your organisation's own policy — review before you make it mandatory.
Get the SCORM package while you are here.
Same course, SCORM 2004. Load it to settle the tracking question — and keep it as a course your people can take after you review it.
Request the package
SCORM 2004 zip. We ask for an email so we know which LMS you are testing — and so we can send the download.